 Anish Ramasekar
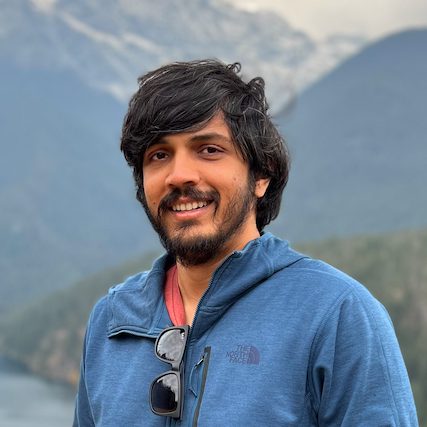
I'm a principal software engineer at Microsoft working on identity and security for Kubernetes and for the AI agents that run on it. I co-chair Kubernetes SIG Auth and have taken features from proposal to GA, including KMS v2 encryption and structured authentication configuration, and I maintained the Secrets Store CSI Driver. Lately I'm building open pieces for agents: durable sessions, sandboxed runtimes and transaction tokens.
What I work on
Kubernetes identity and security
How a cluster decides who a person or workload is and what it may do, from authentication and service account tokens to encrypting secrets at rest.
Features I've shippedSecrets and workload identity
Mounting secrets from external stores into pods, and workload identity on Azure.
Projects I've maintainedInfrastructure for AI agents
Open building blocks for running AI agents: a neutral contract for durable agent sessions, and transaction tokens that carry identity across multi-hop agent calls.
Sessions and transaction tokens
Selected talks
- Secrets Store CSI Driver: Keeping Secrets Secret
Ranked in Top 10 talks at KubeCon EU 2021
Selected posts
For event organizers
Speaker bio
I'm a principal software engineer at Microsoft working on identity and security for Kubernetes and for the AI agents that run on it. I co-chair Kubernetes SIG Auth and have taken features from proposal to GA, including KMS v2 encryption and structured authentication configuration, and I maintained the Secrets Store CSI Driver. Lately I'm building open pieces for agents: durable sessions, sandboxed runtimes and transaction tokens.
Headshot
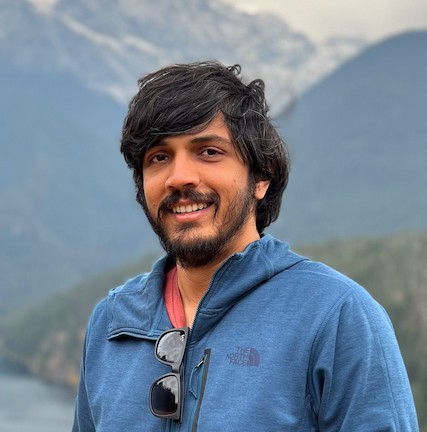 Download headshot
Contact
Email is the best way to reach me. Copy the address if you don't use a mail app on this device.